PHP SECURITY & WEBSITE PROTECTION

Secure Your PHP Website Before Hackers Do.

Protect your business website from malware, outdated PHP versions, security vulnerabilities, and unexpected downtime.

Professional PHP security audits, malware removal, PHP upgrades, and website maintenance by FlowFoundry AI Solutions.

Free Initial Consultation  •  No Obligation  •  Written Quote Before Work
Clear ReportsWritten findings & next steps
Scope-BasedRecommendations per site
Practical FixesActionable remediation plan
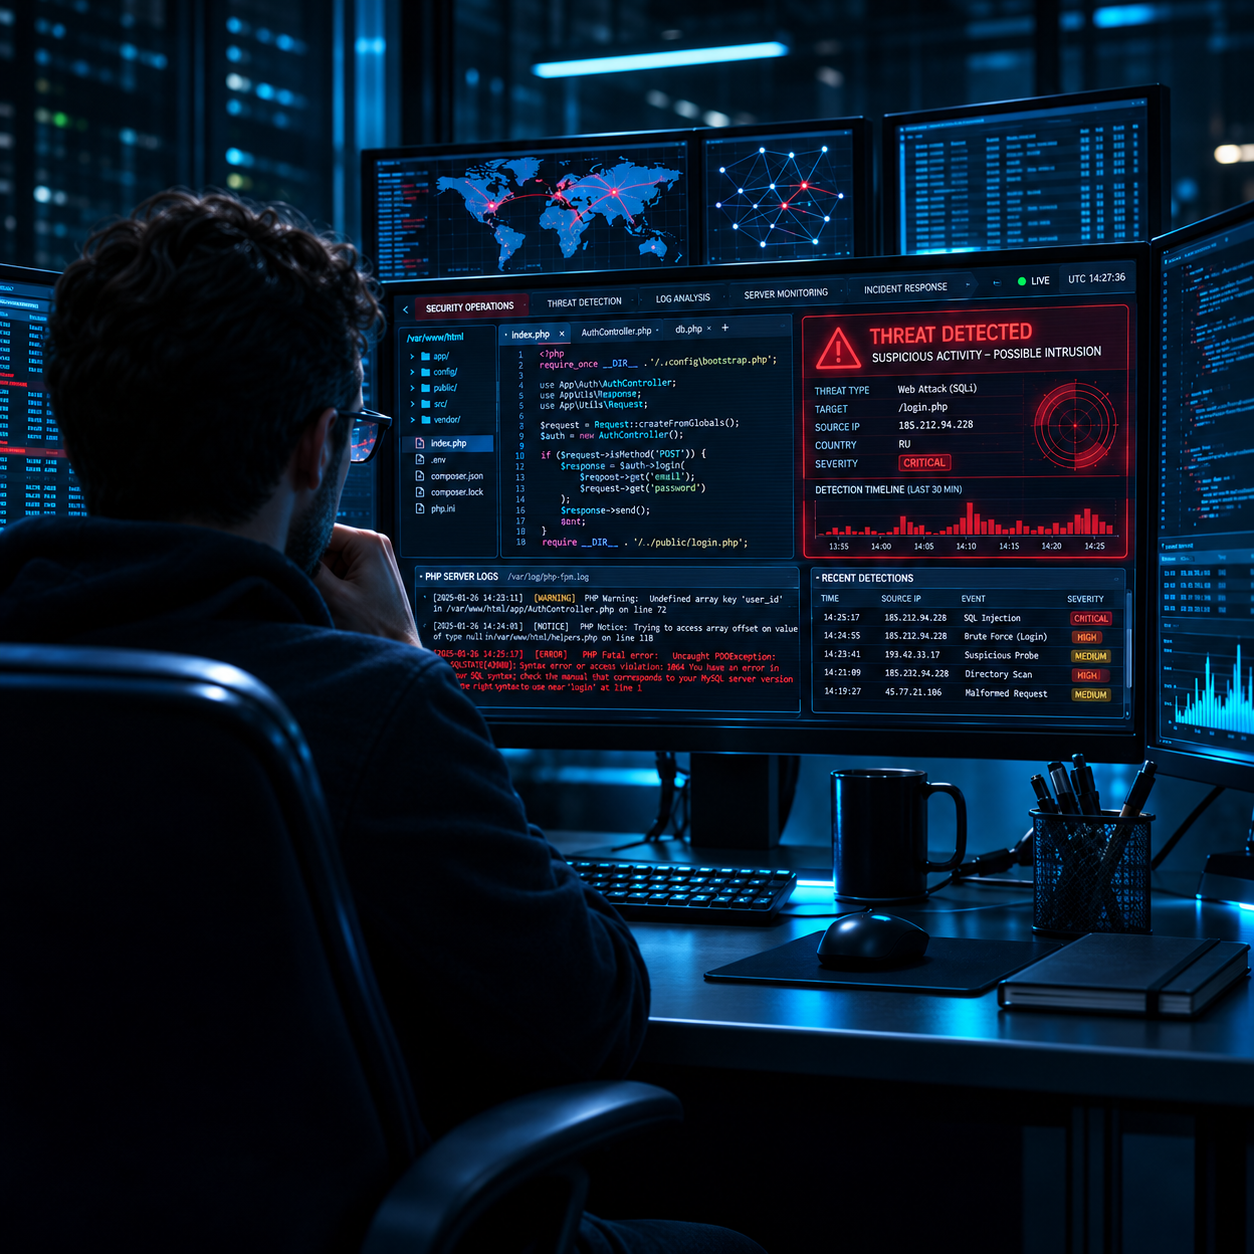
Cybersecurity analyst investigating a PHP website's security posture on a dark operations screen
Security ReviewSigns, symptoms & next steps documented

Platforms We Work With

WordPress WooCommerce Laravel Magento OpenCart Joomla Custom PHP
What We Do

Services Built Around Real Problems

Each engagement is scoped around the site, the reported issue, and a written plan before work begins.

Talk to an Engineer

Security Assessment & Audit

Understand your exposure. An initial scope covers PHP version, publicly observable security headers, HTTPS/TLS configuration, and common exposed configuration checks. Authenticated code reviews or intrusive testing are quoted separately after scope is agreed.

  • PHP version & configuration review
  • Security headers, HTTPS & TLS review
  • Risk summary & recommended next steps
Request assessment scope

Malware Removal & Recovery

If a site is infected or defaced, we triage the issue, remove identified malicious code, and recommend post-cleanup hardening. Final pricing depends on infection severity, access requirements, and recovery complexity.

  • Malicious code & backdoor review
  • Blacklist & remediation guidance
  • Post-cleanup hardening recommendations
Request cleanup scope

PHP Upgrade & Migration

Move from end-of-life PHP 5.6 / 7.x to supported 8.x releases. Deprecated code is refactored, plugins are compatibility-tested, and rollback is prepared on a staging copy. Complex legacy migrations require an individual estimate.

  • Deprecated code fixes & refactoring
  • Plugin & theme compatibility testing
  • Staging-tested with rollback
Request upgrade scope

Website Hardening

Layered defenses tuned to your stack — WAF rules, login protection, file permissions, and security headers. Recommended after assessment or cleanup, based on the risks identified.

  • WAF & brute-force protection
  • Hardened server configuration
  • CSP, HSTS & X-Frame headers
Request hardening scope

Maintenance & Monitoring

Ongoing updates, backups, and malware scans under a defined monthly scope. Incident response work is quoted separately when it exceeds routine maintenance, so expectations stay clear on both sides.

  • Regular core, plugin & dependency updates
  • Offsite backups with restore tests
  • Uptime & malware scan monitoring
Request maintenance scope

Emergency Response

If a site appears compromised or down right now, contact us immediately with the URL and a short description. We triage, contain, and coordinate next steps under a written scope before remediation begins.

  • Priority initial review of the incident
  • Containment & safe-recovery guidance
  • Post-incident summary & recommendations
Report an incident
Our Methodology

From Review to Resilience in 4 Steps

A clear, staging-first engagement flow — you always know what happens next and why.

01

Review

We understand the website, its technology, and any issues you've reported, so the work is grounded in your actual situation.

Discovery
02

Assess

We review the security posture within the agreed scope and identify relevant risks, then document findings and recommended next steps.

Assessment
03

Remediate

Agreed fixes are implemented and functionality is validated before deployment. Rollback is available throughout.

Implementation
04

Maintain

We recommend ongoing monitoring, updates, and maintenance to help keep the site's security posture current.

Ongoing
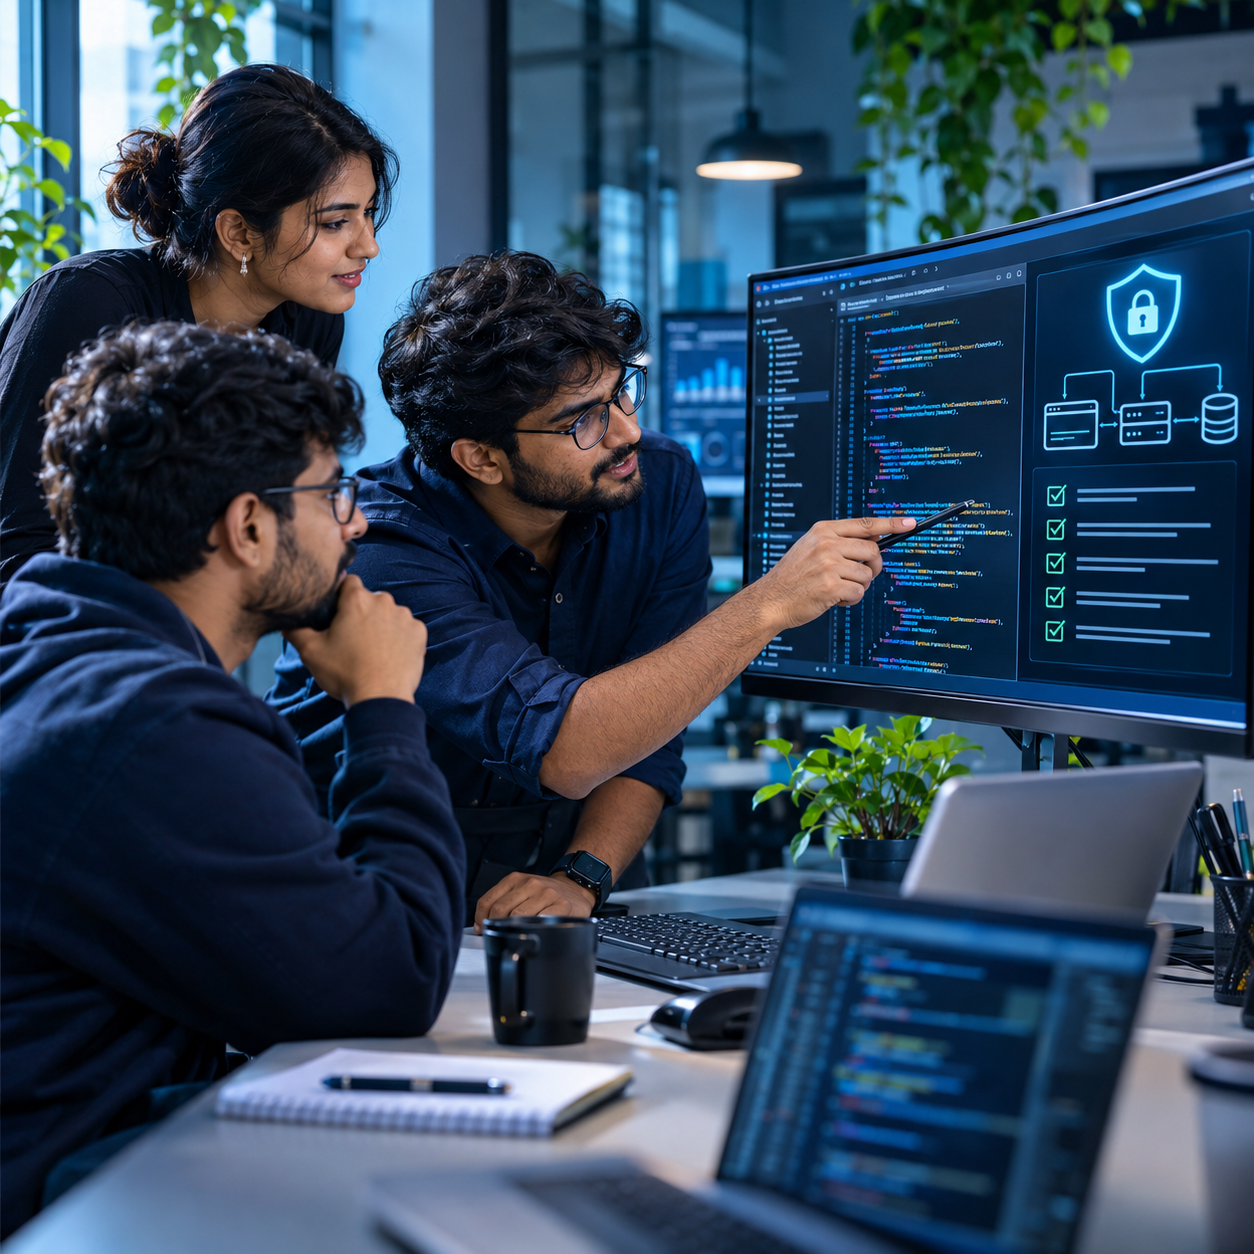
FlowFoundry security engineers reviewing PHP code and hardening a production website
Staging-Tested FixesRollback ready before anything touches production
Why FlowFoundry

Security Engineering You Can Actually Trust

Not a generic agency with a security page bolted on — a focused PHP security team that treats your website like a business-critical asset.

  • Staging-first, alwaysChanges are tested on an isolated copy of your site before deployment, with a documented rollback path.
  • Written scope before you payYou receive a detailed report with fixed pricing before any work begins — no vague estimates, no scope creep, no surprise invoices.
  • Direct technical communicationYou talk directly to the engineers handling your site, via email and WhatsApp, from Vijayawada, serving clients across India and abroad.
  • Clear deliverablesReports, hardening checklists and next-step recommendations are delivered in writing for every engagement.
Clear Assessment ReportsWritten findings delivered per engagement
Scope-Based RecommendationsTailored to your site, not a template
Direct Technical CommunicationEmail & WhatsApp with the engineers
Transparent Pricing

Scope-First, Written Quotes

Starting prices below reflect typical small-to-mid sites. Final pricing depends on website complexity and agreed scope.

One-Time

PHP Security Assessment

Get a clear picture of your website's security posture within an agreed scope.

$36starting at
  • PHP version & configuration review
  • Public security headers & HTTPS/TLS review
  • Common exposed-configuration checks
  • Risk summary + recommended next steps
  • Written report
Request Assessment
Emergency

Malware Cleanup & Recovery

Infection severity, access requirements and recovery complexity determine the final scope.

Custom Quote
  • Triage & written scope first
  • Malicious code & backdoor review
  • Blacklist & remediation guidance
  • Post-cleanup hardening recommendations
  • Report of actions taken
Request Cleanup Quote
One-Time

PHP Upgrade & Migration

Upgrade to a supported PHP release. Complex legacy migrations require an individual estimate.

$72starting at
  • PHP 5.6 / 7.x → 8.2 / 8.3 upgrade
  • Deprecated-function fixes
  • Plugin & theme compatibility pass
  • Staging-first with rollback
  • Performance & OPcache tuning
Request Upgrade

All prices are in USD. Final pricing depends on website complexity and agreed scope. GST invoice provided for all engagements. Maintenance plans have no lock-in — cancel anytime.

Illustrative Security Scenarios

Example Engagement Scenarios

Illustrative Security Scenario — these are composites of the kind of work we perform. They are not customer testimonials or completed case studies.
Illustrative Security ScenarioWooCommerce · PHP 7.2

WooCommerce store flagged by Safe Browsing

The Situation

A retailer is notified that the store has been flagged by Google Safe Browsing. Traffic drops sharply and checkout errors begin appearing.

How We Would Approach This Scenario
  • Isolate the site and capture a forensic copy before changes
  • Identify and remove suspicious code and unauthorized accounts
  • Upgrade PHP, then guide blacklist reconsideration
Possible OutcomeThe store is cleaned, the blacklist removal is guided, and the site is returned to normal traffic — subject to scope and confirmation.
Illustrative Security ScenarioLaravel · Cloud VM

Laravel app with an exposed .env file

The Situation

A B2B dashboard is deployed with APP_DEBUG enabled and a publicly reachable .env file that may contain database and mail API credentials.

How We Would Approach This Scenario
  • Restrict access to config, logs and hidden files
  • Rotate all potentially exposed credentials
  • Add WAF rules, CSP/HSTS headers, and a deploy checklist
Possible OutcomeExposure is closed and credentials rotated before misuse, with a documented deployment checklist.
Illustrative Security ScenarioCustom PHP · Shared Hosting

Legacy custom CMS repeatedly defaced

The Situation

A regional news portal runs a hand-built PHP 5.4 CMS. Defacements recur every few months despite file restorations.

How We Would Approach This Scenario
  • Assess and migrate to a supported PHP version
  • Review authentication and database access patterns
  • Recommend an ongoing maintenance & monitoring plan
Possible OutcomeA stable, supported stack with monitoring and a maintenance cadence — reducing recurrence risk.

Your business is unique. Every engagement is scoped and quoted in writing before work begins — these illustrative scenarios show how a typical engagement could unfold, not a guarantee of identical results.

See What a Security Assessment Includes

A Clear, Labeled Sample Report

Explore a clearly labeled sample report showing how potential security risks, findings, and recommended actions can be documented.

SAMPLE REPORT — Illustrative Data Only

Sample Security Assessment

This is a demonstration of the report structure we deliver. Data shown is fictional or from a local test environment and does not reflect any real website.

Assessment OverviewBaseline review of a demo site, scoped to passive checks only.
Website TechnologyPHP-based CMS (demo), typical plugin set.
PHP Version ReviewOutdated — action recommended
Security HeadersPartial — several missing
HTTPS ConfigurationValid certificate, HSTS missing
Risk Severity ModelHigh · Medium · Low · Informational
  • Example Finding 1 — HighOutdated PHP runtime no longer receives security updates. Recommended next step: plan an upgrade to a supported release.
  • Example Finding 2 — MediumMissing Content-Security-Policy and Strict-Transport-Security headers. Recommended next step: add headers after confirming compatibility.
  • Example Finding 3 — InformationalDirectory listing enabled on a non-sensitive path. Recommended next step: disable for defense in depth.
Recommended ActionsPrioritized remediation plan with effort notes.
Assessment LimitationsPassive-only scope. No authenticated code review or intrusive testing performed.

The sample report above is illustrative. Authenticated code reviews, file-level scanning, and intrusive security testing are separate scope items and are quoted individually after a discussion.

What You Receive

Concrete Deliverables, Every Time

No vague "we secured it" emails. You walk away with documentation and a plan.

Written Report

Findings, severity notes and recommended next steps in a single written document.

Action Summary

What was changed, what still needs a decision, and which options remain open.

Hardening Notes

Configuration changes documented and reversible, so the environment stays understandable.

Backup & Rollback Notes

Backup and rollback guidance where applicable, so future changes stay recoverable.

Maintenance Summary

For ongoing clients, a monthly summary of updates, scans and relevant notes.

Direct Technical Contact

Email and WhatsApp access to the engineers working on your site — no ticket queues.

Staging-first testing on every change Written confirmation of scope before payment Zero-surprise billing, always
Questions & Answers

Straight Answers, Before You Ask

Everything businesses usually want to know before trusting us with their website.

Dark server room at night with glowing warning lights representing active website threats
If Something Looks Wrong, Act Now

Every Hour Your Site Stays Hacked
Costs You Customers

Defacement, blacklists, stolen data, lost rankings — they compound by the hour. Message us now and get an engineer on your case today.

Prefer email? Reach us at info@flowfoundryai.in — we reply during business hours.

No contracts Written quotes first NDA on request GST invoice provided
Get In Touch

Let's Secure Your Website

Concerned about malware, outdated PHP, or website vulnerabilities? Contact our team for an initial consultation and receive guidance on the next steps.

Email Our Security Team

Share your website URL and a short description of what you're seeing. We reply during business hours with next-step guidance.

info@flowfoundryai.in

Chat on WhatsApp

Fastest way to start. Send your website URL and a brief description — we'll reply during business hours.

Business hours: Mon–Sat, 9:00–19:00 IST · Email: info@flowfoundryai.in · WhatsApp: +91 73309 37354
Please do not send passwords, server credentials, or API keys by email. Secure access arrangements are provided when required.
Chat with an engineer — +91 73309 37354